Quantum communication is not a faster replacement for the internet, and it does not make every message automatically unbreakable. It is a set of technologies that uses quantum states—often individual particles of light—to do specialised things that normal networks cannot. One important use is quantum key distribution (QKD): helping two parties create a shared secret key while checking whether the quantum exchange was disturbed. A broader, still-developing goal is to connect quantum devices by sending quantum states or distributing entanglement. The urgent security issue for most people and organisations is related but different: post-quantum cryptography (PQC). PQC uses new, quantum-resistant mathematical algorithms on ordinary computers and networks. It is designed to replace public-key cryptography that a sufficiently capable future quantum computer could break. In practical security planning, PQC and QKD are alternatives or complements in specific architectures—not interchangeable labels for the same thing.
This article is part of the software engineering technologies guide library.
Key takeaways
Quantum communication uses quantum states for specialised communication or networking tasks; it is not a consumer replacement for Wi-Fi, mobile data or the public internet.[1] [10]
QKD distributes cryptographic key material. It does not itself encrypt an email, authenticate every party, or protect a whole network by itself.[1] [3]
Post-quantum cryptography runs on conventional systems. NIST finalised its first three core PQC standards in August 2024, including ML-KEM for key establishment and two digital-signature standards.[5] [6]
The timing of a cryptographically relevant quantum computer is unknown. Migration work matters now because discovering cryptography dependencies and updating systems can take years.[2] [5]
Real QKD deployments carry physical and operational trade-offs: specialised equipment, distance loss, authentication requirements, trusted-node risks in some designs, implementation flaws and denial-of-service exposure.[3]
India context, date-sensitive: the National Quantum Mission includes a Quantum Communication T-Hub and states objectives around QKD links and PQC; India Mobile Congress 2026 listed Quantum Communications among its programme themes.[7] [9]
What quantum communication means
A normal network transmits classical bits: each bit is read as a 0 or a 1. Quantum communication handles information encoded in quantum states, commonly optical states of single photons. Measuring an unknown quantum state can disturb it, and an unknown quantum state cannot simply be copied perfectly. Those properties can be useful for security protocols and for linking future quantum devices, but they also make the engineering difficult.
NIST defines a quantum network as quantum nodes connected by quantum communication channels and supporting classical channels for functions such as timing, stabilisation and routing.[1] That last point is easy to miss: a quantum network does not eliminate conventional networking. It depends on it.
### Three things often grouped under one label
QKD is the most widely discussed near-term application. It creates shared secret keys that conventional symmetric encryption can then use.
Quantum networking is broader. It aims to transmit quantum states or distribute entanglement between nodes. Potential research uses include linking quantum processors and distributed quantum sensing.[10]
Post-quantum cryptography is neither a photon network nor quantum computing. It is conventional cryptography designed to resist attacks from both conventional computers and an anticipated class of powerful quantum computers.[2]
Plain-English distinction: QKD changes how a secret key can be established over a specially engineered link. PQC changes the mathematics used by security software and protocols on existing digital infrastructure.
How quantum key distribution works
QKD is best understood as a key-establishment protocol, not a magic encryption pipe. Different QKD protocols exist, but the basic logic is similar.
### 1. Send quantum states
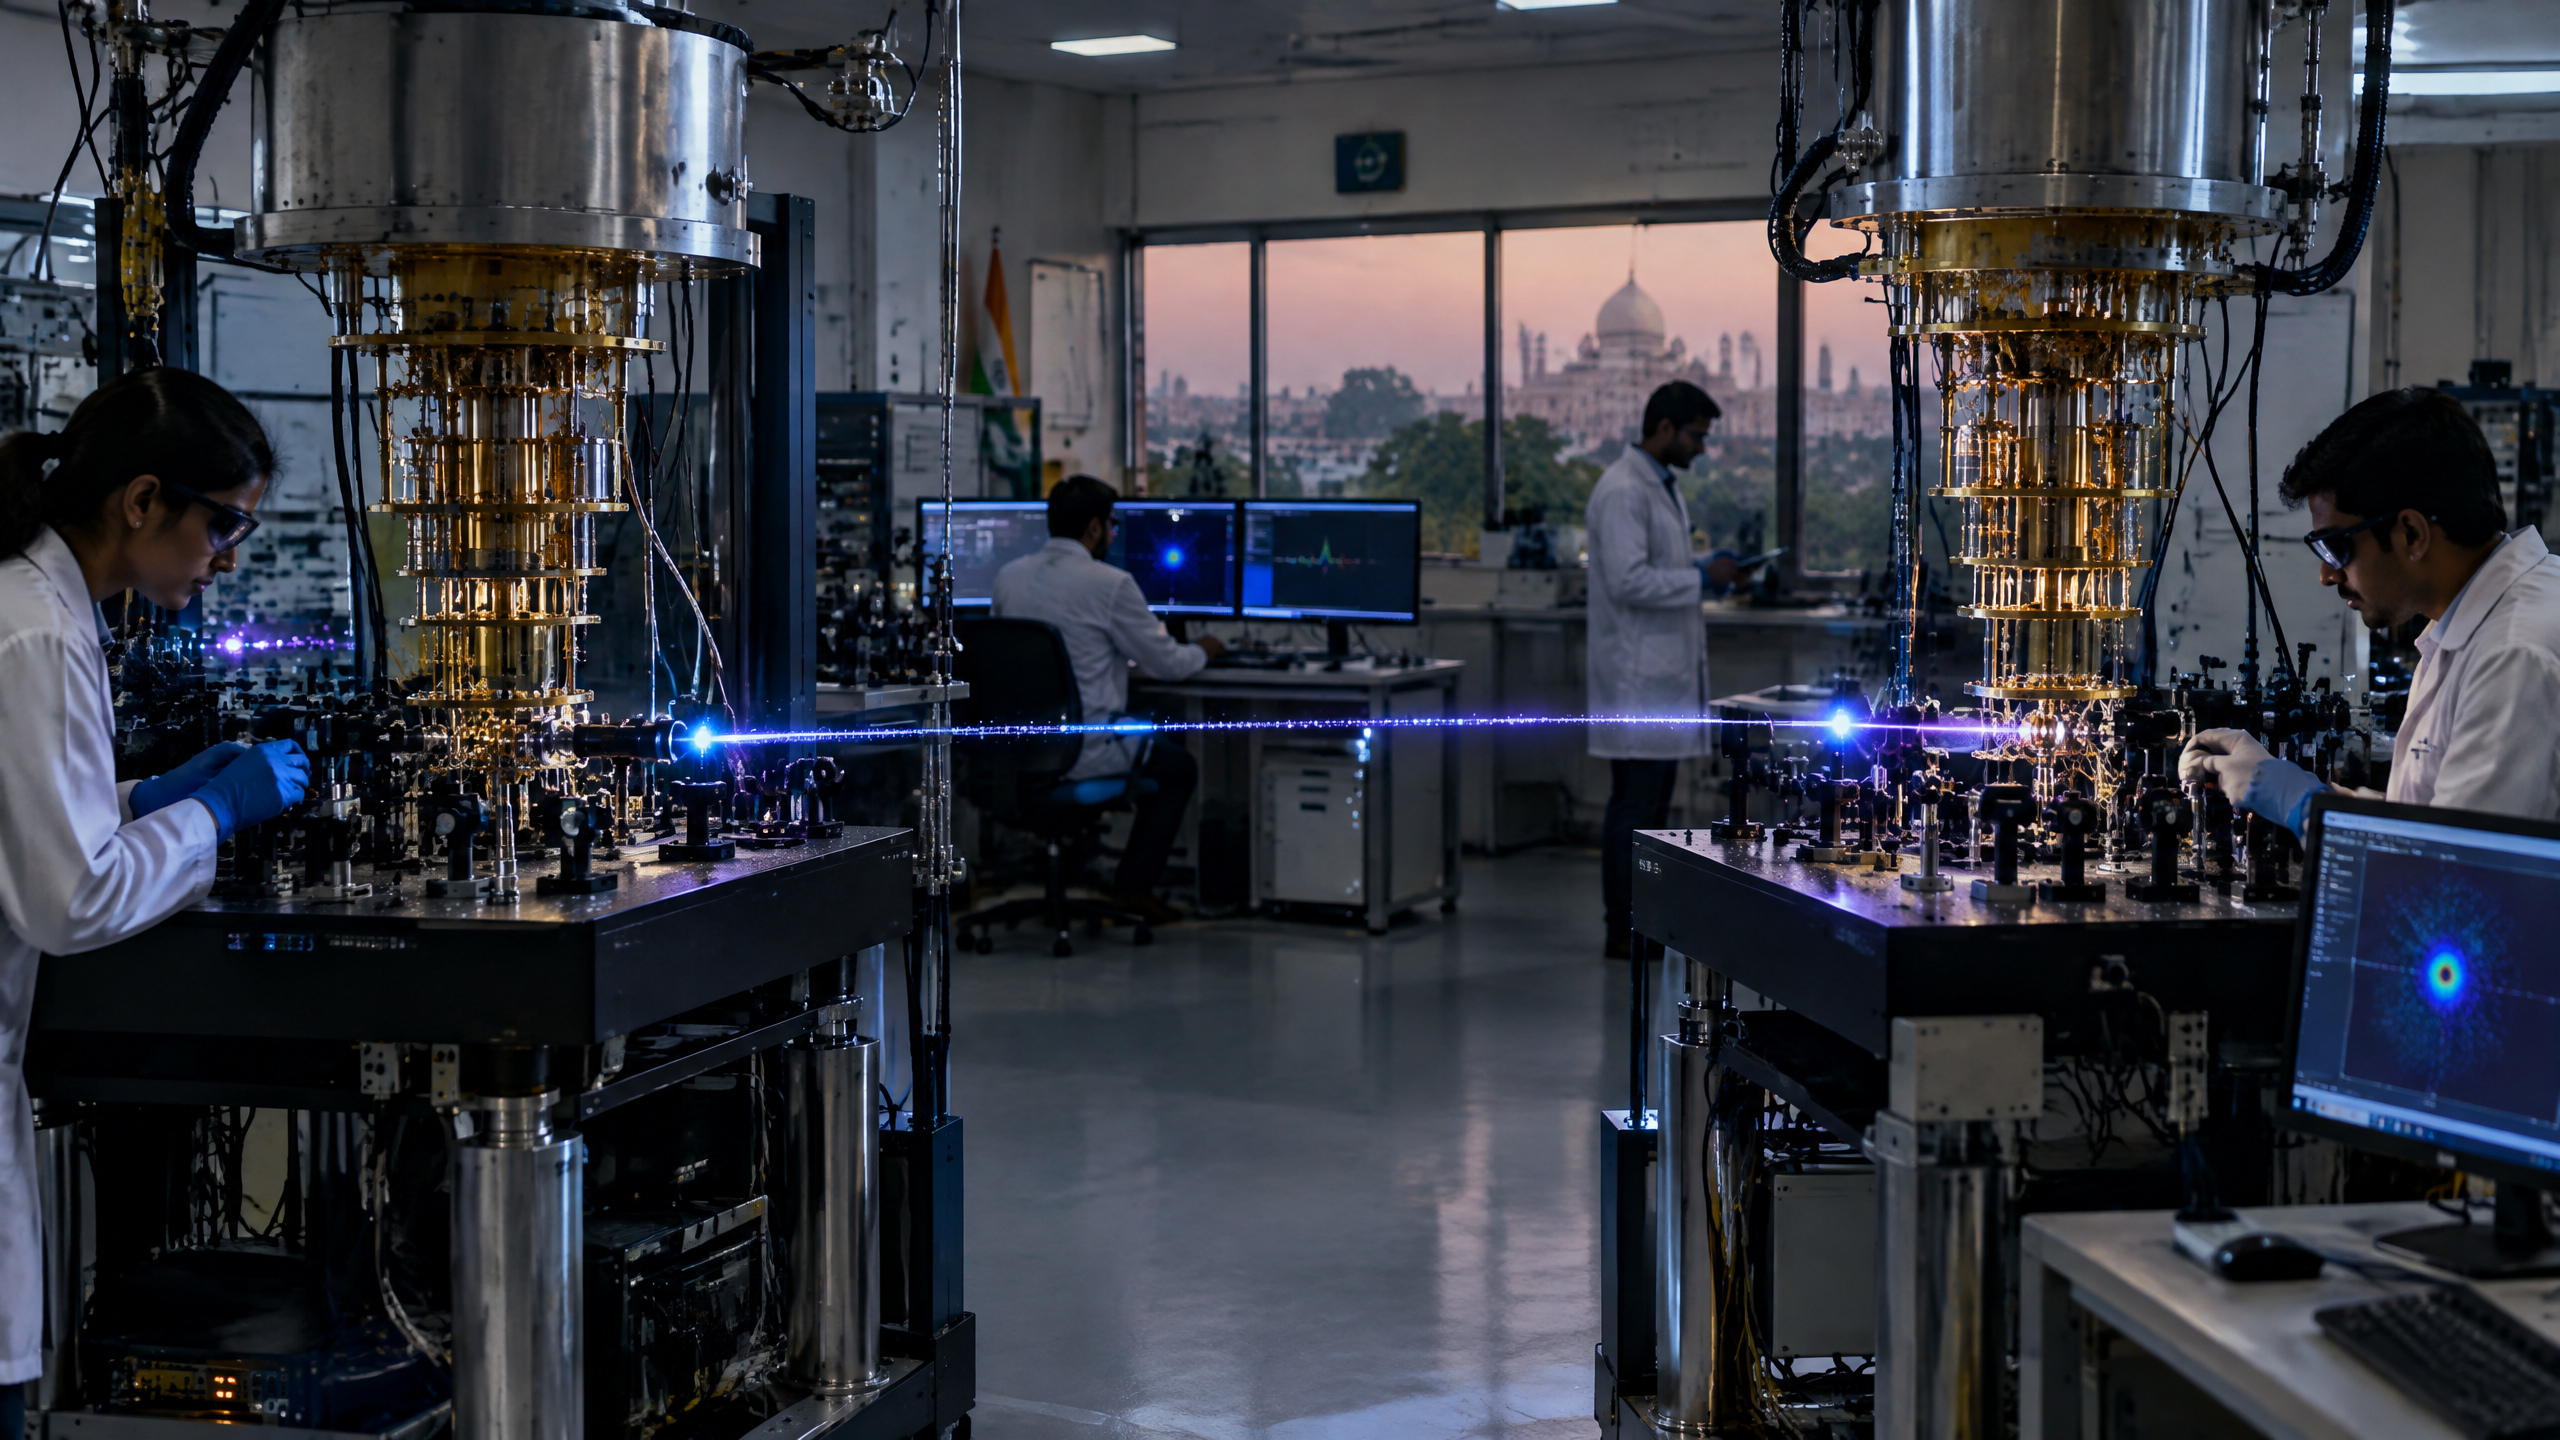
One endpoint prepares quantum states—for example, photons prepared using randomly chosen settings—and sends them across a quantum channel, such as dedicated fibre or a free-space optical path. The receiving endpoint measures them using randomly chosen settings.
### 2. Compare selected information over a classical channel
The endpoints publicly discuss limited metadata, such as which settings they used, without revealing the final candidate key. They retain measurement results that are compatible according to the protocol.
### 3. Check for excess errors
They disclose and compare a small sample. An interceptor who measures the quantum states generally creates detectable disturbance. If the measured error level is too high, the attempt is discarded. If it is acceptable, the parties apply error correction and privacy amplification to produce a shorter shared key.
### 4. Use the final key with ordinary cryptography
The resulting key can feed a symmetric encryption system that protects data. The application data still travels through conventional systems; QKD does not turn the content itself into a quantum message.
This model explains both QKD’s appeal and its boundary. Its detection property concerns the quantum exchange under stated assumptions. It is not a guarantee that every component, endpoint, operator, software integration or denial-of-service scenario is secure. NIST describes QKD as a family of protocols for generating secret keys, while the U.S. National Security Agency (NSA) stresses that practical QKD security is highly dependent on implementation.[1] [3]
### Why authentication cannot be skipped
A QKD system also needs an authenticated classical channel. Without a way to confirm who is at the other end, an attacker could impersonate each party to the other. The NSA notes that QKD does not provide source authentication for the QKD transmission on its own; authentication therefore needs pre-shared keys or asymmetric cryptography.[3]
That is why phrases such as “QKD makes communications unhackable” are misleading. QKD can be one component in a carefully designed system. It does not remove identity, endpoint, key-management, physical-security or operations problems.
QKD versus post-quantum cryptography
The two approaches address part of the same long-term concern, but their deployment models are very different.
### Post-quantum cryptography: software and protocol migration
Much of today’s public-key cryptography relies on mathematical problems that are hard for conventional computers. A sufficiently capable quantum computer could undermine important widely used public-key approaches. PQC uses different mathematical problems believed to be hard for both conventional and quantum computers.[2]
Observed status, current as of 13 October 2026: NIST’s first principal PQC standards are FIPS 203 (ML-KEM), FIPS 204 (ML-DSA) and FIPS 205 (SLH-DSA). ML-KEM is a key-encapsulation mechanism: under specified conditions, two parties can establish a shared secret over a public channel, then use it with symmetric cryptography for secure communication tasks.[4] [5]
PQC does not require quantum links, quantum repeaters or quantum hardware in the field. Its hard work is migration: identifying where vulnerable algorithms live in certificates, hardware, APIs, VPNs, code-signing systems, devices, vendors and archived data; testing interoperability and performance; and preparing for algorithm changes. NIST says organisations should begin applying the standards and notes a transition plan that phases out quantum-vulnerable algorithms from its standards by 2035, with high-risk systems moving sooner.[5]
### QKD: a specialised physical link
QKD’s premise is different. It establishes keys through quantum signals and physical-layer equipment. This can be relevant to high-assurance, point-to-point or research use cases where the operational model justifies dedicated infrastructure. It is not a drop-in software update for a general enterprise network.
The NSA’s published assessment for U.S. national security systems concludes that quantum-resistant cryptography is more cost-effective and easier to maintain than QKD, unless QKD’s stated limitations are overcome. This is an institutional security position in that context, not evidence that QKD research has no value or that every QKD use case is identical.[3]
### A useful decision lens
For a general organisation, the starting question is usually not “Where can we buy a quantum link?” It is “Which cryptographic dependencies must become crypto-agile, and which data or systems have long confidentiality lives?” That framing points first toward inventory, migration planning and standardised PQC.
For a narrowly scoped, high-assurance connection, a team may separately evaluate whether a QKD architecture is technically and economically justified. That evaluation must include authentication, trusted nodes, physical routes, operations, vendor interfaces and recovery procedures—not only the theoretical protocol.
The real limits: what quantum communication cannot promise
Quantum technology is often described in absolutes. The real picture is more useful.
### Loss and distance are physical constraints
Photons are lost in fibre and free-space links can be affected by alignment and environmental conditions. The quantum states used in networking are fragile. NIST notes that quantum states decay exponentially with transmission distance because of loss; quantum repeaters are a proposed way to mitigate the problem, but require demanding components such as quantum memories, interfaces, photon sources and detectors.[1] [8]
A long-distance research demonstration is therefore meaningful evidence of engineering progress, not proof of a nationwide, general-purpose quantum internet.
### QKD equipment is specialised
The NSA identifies the need for dedicated fibre or managed free-space transmitters as a central QKD constraint. It says QKD cannot simply be deployed as software or as a generic network service and is not easily integrated into existing equipment.[3]
This creates cost, maintenance and upgrade consequences. A vulnerability in a classical software library may be patched comparatively quickly. Physical devices, optical paths and tightly coupled integrations can make change slower and more expensive.
### Trusted relays can move the trust problem
A direct quantum link cannot necessarily span every desired distance. Some QKD networks use intermediate trusted nodes that access key material and relay it onward. The NSA highlights both added infrastructure cost and insider-risk exposure in such models.[3]
This is not a minor footnote. It means an architecture marketed as “quantum-secure” still needs a clear trust diagram: who can access keys, which sites are physically protected and what happens if one intermediary is compromised.
### Quantum key distribution does not stop denial of service
An eavesdropping attempt may cause errors that prompt endpoints to abort a QKD session. That detection can be useful, but it also gives an attacker a way to disrupt availability. The NSA identifies denial of service as a significant risk because of QKD’s sensitivity to interference.[3]
Security has multiple goals: confidentiality, integrity, authentication and availability. A technology can strengthen one part of a system while leaving another difficult.
### A quantum network is not the quantum internet—yet
The phrase quantum internet usually describes an aspirational network able to distribute quantum states or entanglement among many nodes. It should not be used as if it were a replacement for today’s packet-switched internet.
A 2024 National Quantum Initiative Advisory Committee report states that quantum networks will not replace classical networks and currently cannot match the data rates or packet-switching capabilities that define today’s internet. It also says the scale of quantum networking’s eventual role will become clearer through sustained research and development.[10]
Interpretation: the near-term value of quantum communication is most credible when linked to a specific task—key distribution, a testbed, a quantum-device link or sensing research—rather than a vague promise of universally superior networking.
Why post-quantum security matters before a quantum computer arrives
No one knows when, or whether, a quantum computer capable of breaking current public-key systems will exist. NIST describes the field as still facing major technical hurdles and says estimates range from years to decades.[2] Treating a predicted date as settled fact would be misleading.
The reason to act before that date is the harvest-now, decrypt-later risk. An adversary can collect encrypted traffic or data today and attempt to decrypt it later if the protection becomes breakable and the data remains valuable. NIST also observes that integrating new algorithms throughout information systems historically can take 10 to 20 years.[2]
That does not mean every password, file or connection needs a dramatic immediate rebuild. It does mean organisations should distinguish data by confidentiality lifetime, identify cryptography dependencies and design systems that can replace algorithms without redesigning everything. That capability is often called cryptographic agility.
India context: research, infrastructure and careful claims
Observed status, current as of 13 October 2026: India’s National Quantum Mission is a Department of Science and Technology programme running from 2023–24 to 2030–31. Its Quantum Communication T-Hub is hosted by IIT Madras and C-DOT. The mission site lists work on satellite and terrestrial secure-key-distribution channels and includes stated targets for satellite-based QKD links, metropolitan fibre grids and PQC cryptosystems.[7] [8]
India Mobile Congress 2026 also listed Quantum Communications within its future-building technology themes and included a Quantum Summit on its agenda.[9] This establishes quantum communication as a visible policy and industry discussion area. It is not, by itself, evidence that QKD is widely available to consumers or businesses across India.
A government press release dated 5 November 2025 reported that a DST-supported startup demonstrated a QKD network spanning more than 500 km over an optical-fibre testbed in the Rajasthan sector. The release says the trial used two trusted nodes for end-to-end key exchange.[11] This is a concrete, date-stamped demonstration, not a basis for claiming a generally available national quantum network.
For Indian organisations, the practical implication is similar to the global one: follow standardised PQC migration developments while treating specialised quantum links as an architecture question with location, fibre, hardware, operations and assurance constraints. Requirements in regulated sectors can be material, but this article does not offer legal, procurement or compliance advice.
What a sensible quantum-security plan looks like
For most technical teams, a grounded plan is less glamorous than a “quantum-proof” announcement:
Inventory cryptography. Locate public-key algorithms in applications, certificates, appliances, firmware, developer tools, third-party services and backups.
Classify long-lived data. Identify records or communications that may need confidentiality beyond the useful life of current public-key cryptography.
Plan for crypto agility. Prefer systems that can change algorithms, keys and certificate handling with controlled testing rather than full platform replacement.
Track standards and vendor evidence. Use final standards and documented interoperability results; do not mistake a marketing label for a migration plan.
Evaluate QKD only against a defined architecture. Include authentication, endpoint protection, fibre or free-space path, trusted-node model, service availability, patching, monitoring and exit strategy.
These are general engineering considerations, not a prescription that every reader should deploy QKD or switch an entire environment at once.
Frequently asked questions
### Is quantum communication the same as quantum computing?
No. Quantum computing uses quantum states to perform certain computations. Quantum communication uses quantum states to establish keys, transfer quantum information or distribute entanglement between systems. The fields can support one another, but they solve different problems.[1] [2]
### Is QKD a type of encryption?
Not in the usual sense. QKD is a method for establishing shared secret key material. A conventional symmetric cipher then uses that key to encrypt data. QKD alone does not encrypt the message content or solve authentication.[1] [3]
### Can QKD detect every hacker?
No. In an ideal protocol, interception of quantum states can create detectable disturbance. Practical protection depends on the full implementation, including devices, authentication, endpoints, network operations and physical security. It also does not prevent all denial-of-service attacks.[3]
### Does QKD make a connection unbreakable?
That is too strong. Theoretical properties of a protocol do not guarantee that a deployed system has no implementation flaws or operational weaknesses. The NSA specifically cautions that practical QKD security is implementation-dependent.[3]
### What is post-quantum cryptography in simple terms?
PQC is new cryptography designed to run on ordinary computers while resisting attacks from both ordinary computers and a sufficiently capable future quantum computer. It is intended to replace vulnerable public-key algorithms in software, protocols and products.[2] [5]
### Has NIST finalised post-quantum standards?
Yes. As of 13 October 2026, NIST’s first three final PQC standards are FIPS 203 for ML-KEM, FIPS 204 for ML-DSA and FIPS 205 for SLH-DSA. NIST continues to standardise additional options and backups.[5] [6]
### Will quantum networks replace the internet?
No evidence supports treating that as the near-term outcome. Quantum networking is expected to complement classical networks for specialised capabilities, not match their general-purpose data rates and packet switching.[10]
### Is quantum communication available across India?
A broad consumer or nationwide availability claim would be unsupported. India has mission-led research and development activity, and official releases describe dated QKD demonstrations. Availability depends on a particular project, route, architecture and provider, so it must be verified case by case.[7] [11]
Same-site internal-link recommendations
Link “post-quantum security” to /article/ai-security-platforms-model-prompt-agent-protection when explaining security governance and migration ownership.
Link “data in use and key management” to /article/confidential-computing-data-in-use-security for readers comparing security controls across a system.
Link “zero trust and authentication” to /article/zero-trust-security-explained when discussing why QKD does not replace identity controls.
Link “6G and telecom research” to /article/6g-technology-intelligent-ran-india from the India technology context.
Link “satellite links” to /article/satellite-internet-ntn-direct-to-device-networks to distinguish quantum satellite experiments from consumer satellite connectivity.
Link “AI and hardware infrastructure” to /article/ai-infrastructure-gpus-tpus-npus-inference-energy only as a contextual comparison of different advanced-computing infrastructure—not as a claim that AI infrastructure is quantum networking.
Frequently asked questions about Quantum Communication Explained: QKD, Post-Quantum Security and Real Limits
These answers summarise the scope of this explainer. Availability, standards and implementation details can change, so check current official guidance before acting.
What is Quantum Communication Explained: QKD, Post-Quantum Security and Real Limits?
Quantum Communication Explained: QKD, Post-Quantum Security and Real Limits explains the main ideas, practical uses and limitations in plain English.
Why does this technology matter?
Its value depends on the problem, implementation, evidence, cost, security and the people responsible for using it.
What should readers verify?
Verify current availability, compatibility, security, privacy and regulatory details with the relevant official source.
Is this article professional or legal advice?
No. It is general technology information and does not replace professional, legal, regulatory or security advice.
Source notes
Reporting record
techduopulse stores source destinations privately. Public notes remain non-clickable so every visitor journey stays on this website.
India Mobile Congress 2026 official programme
Primary source · Research source 9Quantum Networks at NIST: Glossary
Primary source · Research source 1What Is Post-Quantum Cryptography?
Primary source · Research source 2Quantum Key Distribution (QKD) and Quantum Cryptography (QC)
Primary source · Research source 3FIPS 203: Module-Lattice-Based Key-Encapsulation Mechanism Standard
Primary source · Research source 4NIST Post-Quantum Cryptography Project
Primary source · Research source 5NIST Releases First 3 Finalized Post-Quantum Encryption Standards
Primary source · Research source 6National Quantum Mission — Government of India
Primary source · Research source 7National Quantum Mission: Mission Verticals and Thematic Hubs
Primary source · Research source 8National Quantum Initiative Advisory Committee: Quantum Networking Findings and Recommendations
Primary source · Research source 10DST-Supported Startup Demonstrates 500 km Quantum-Safe Network
Primary source · Research source 11New India-focused explainer covering quantum communication explained, practical context, limitations and verified sources.