SEO title: Confidential Computing Explained: Protecting Data in Use Meta description: Confidential computing protects sensitive data while it is processed. Learn how trusted execution environments, attestation, limitations, and India’s data-security context fit together. Primary keyword: confidential computing explained
This article is part of the software engineering technologies guide library.
What is confidential computing?
Confidential computing is a hardware-based approach to protecting data and, in many designs, code while they are actively being processed. The Confidential Computing Consortium defines it as performing computation in a hardware-based, attested TEE. In that model, the TEE isolates the chosen workload from other software that would normally have powerful access to the machine. [1]
A useful way to frame the problem is through three data states:
Data at rest is stored in a database, disk, backup, or object store.
Data in transit is moving between systems or services.
Data in use is being loaded into memory and operated on by a processor.
Encryption for files and network connections remains necessary. Confidential computing addresses the third state, where ordinary application processing may otherwise expose readable material to a larger part of the computing stack. [1]
NIST describes hardware-enabled security as a foundation for a layered cloud and edge security strategy. That is the appropriate mental model: confidential computing is a control that can make one important trust boundary narrower; it is not a replacement for the controls above and below it. [2]
Why encryption at rest and in transit is not the whole story
Consider a service that receives an encrypted record, decrypts it, calculates a result, and saves the result. TLS can protect the trip to the service. Storage encryption can protect the saved file. Yet the service must still hold the record in a usable form as it performs the calculation.
In a conventional environment, the operating system, hypervisor, privileged administrators, and other infrastructure layers are part of the trust picture for that active processing. A confidential-computing design aims to keep selected data and code inside an isolated execution area so that other host software has less ability to inspect or alter them. The exact protection depends on the hardware architecture, firmware, configuration, and workload design. [1] [3]
This is especially relevant when an organisation needs to run a sensitive workload on infrastructure operated by another team or provider. It may also matter when separate tenants share a physical platform. But the technology does not remove the need to decide whether the workload should process the data in the first place, who is allowed to request it, or what the application is permitted to return.
How confidential computing works
### A trusted execution environment creates a smaller boundary
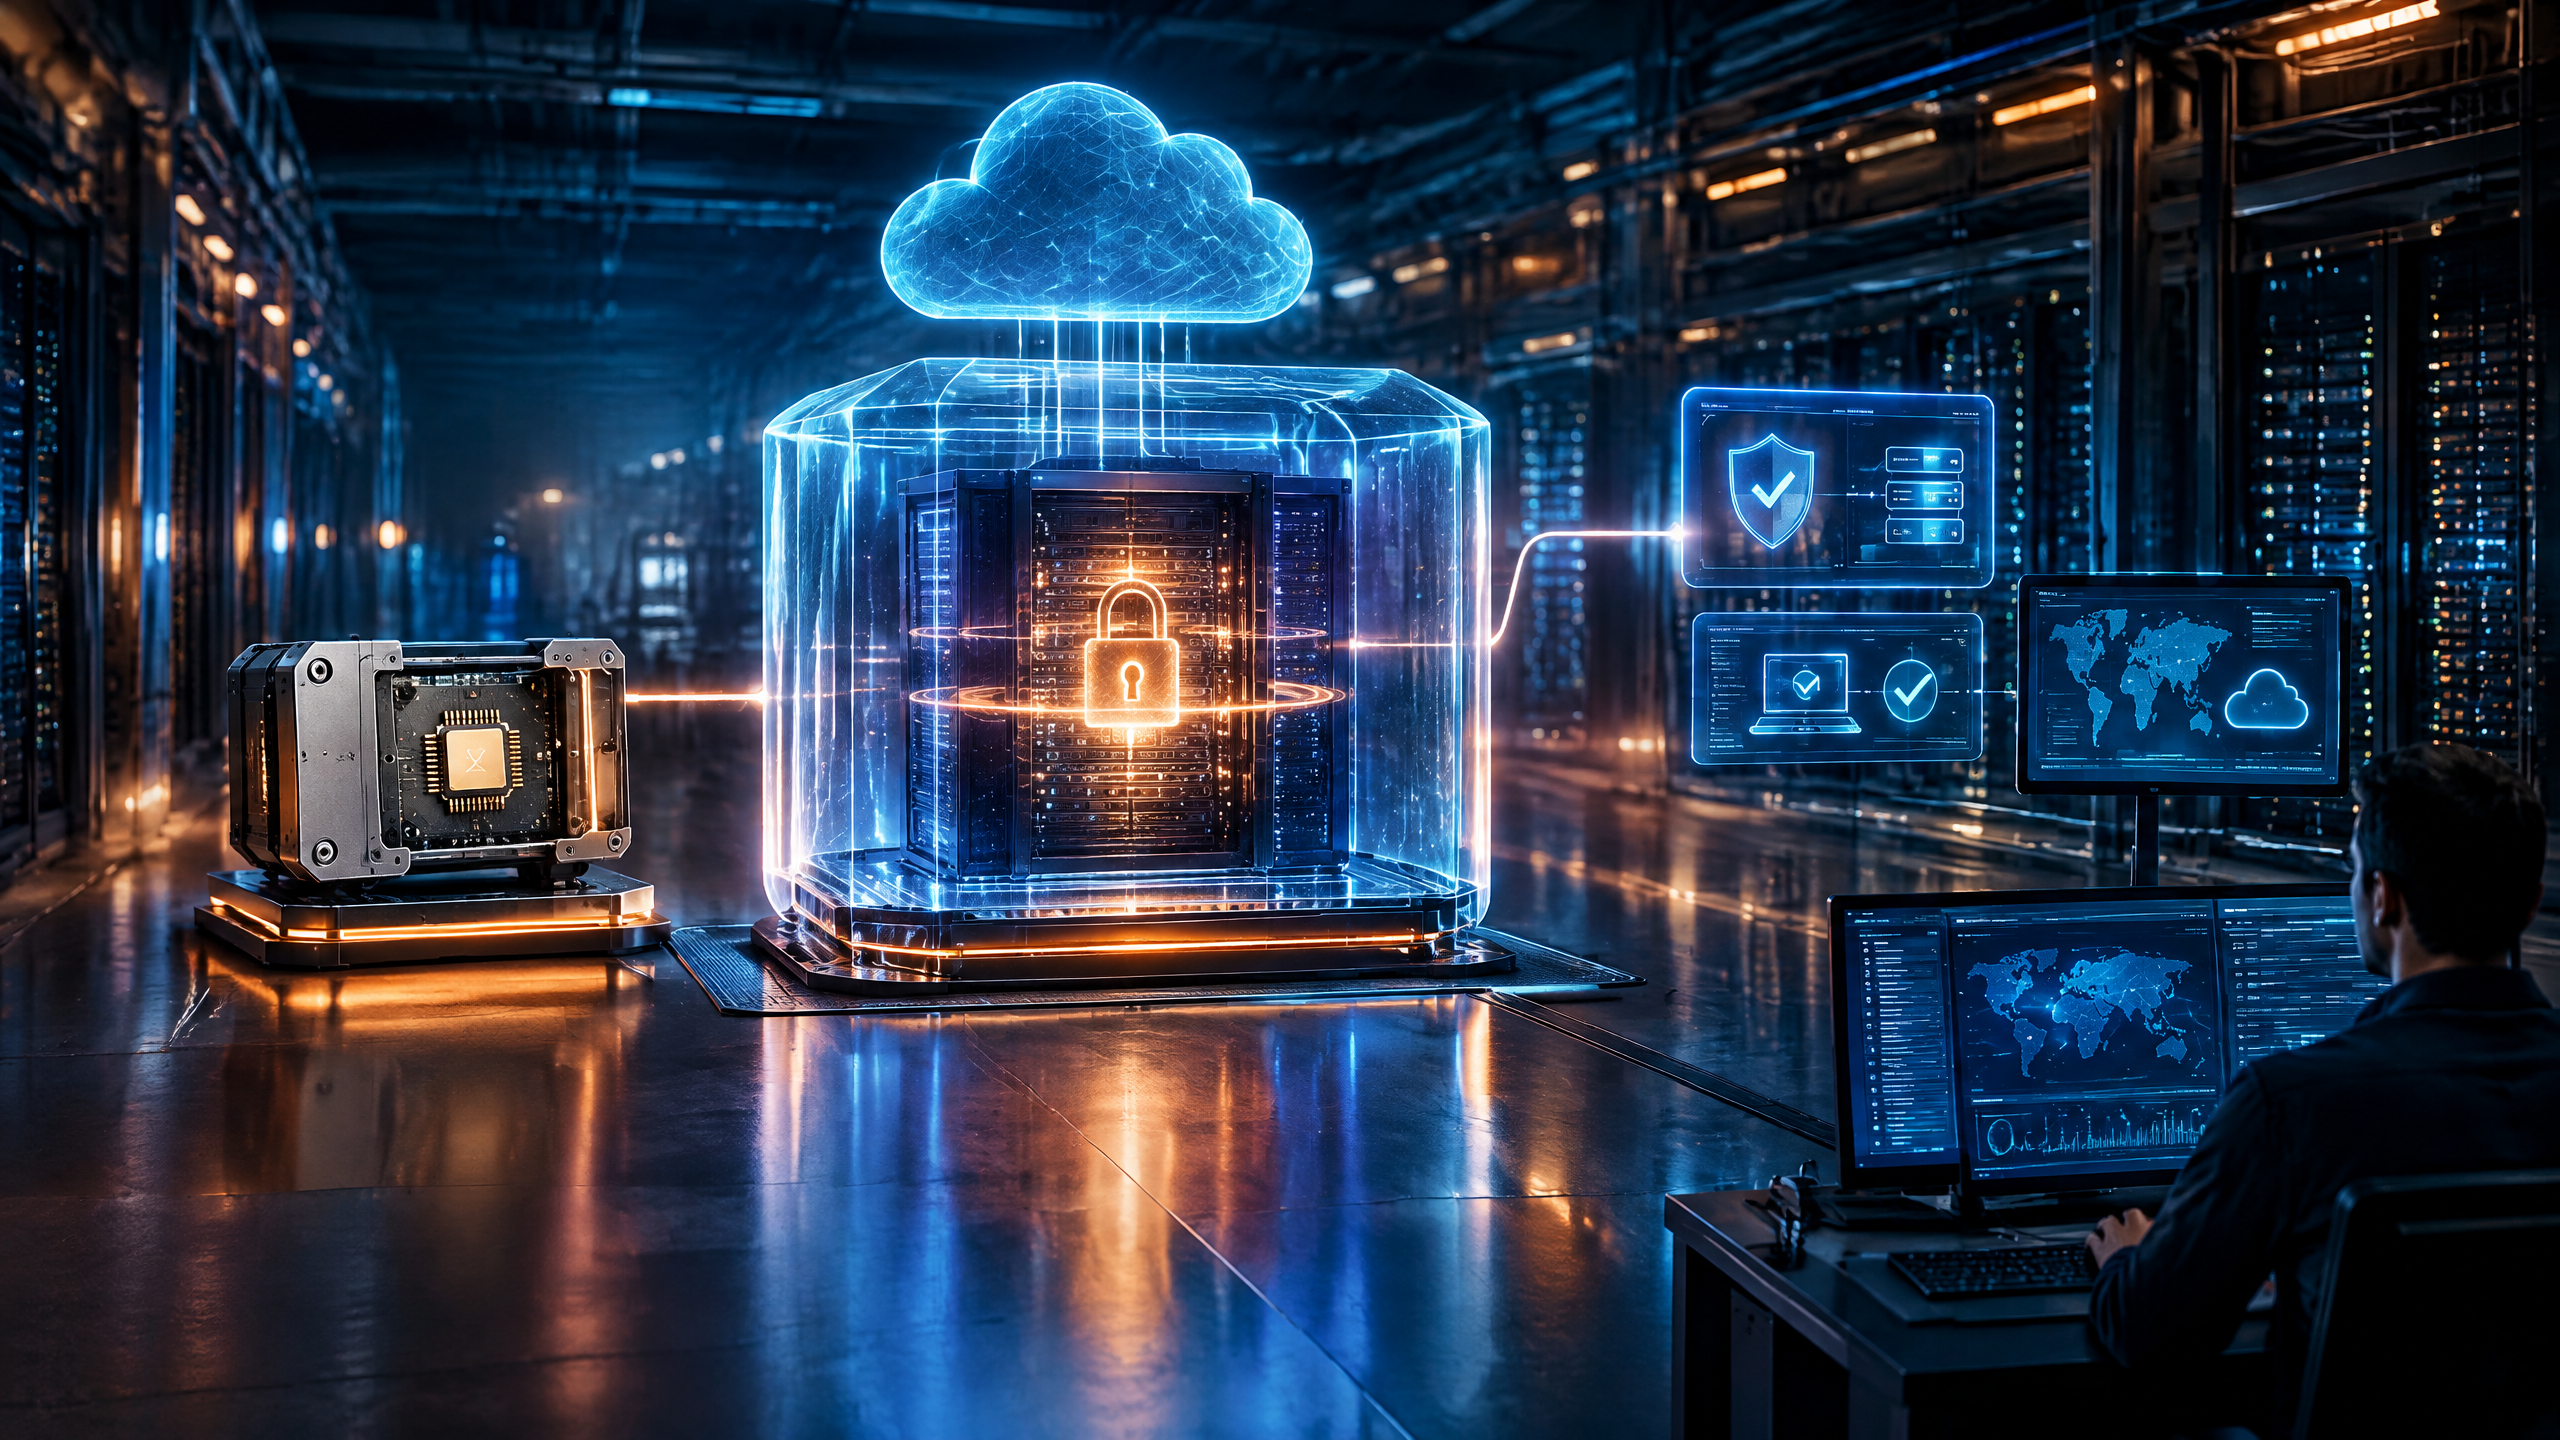
A trusted execution environment (TEE) is an isolated area for executing selected code and handling its data. In a TEE-based design, the processor and related platform components enforce a boundary that separates the protected workload from other software on the host. NIST’s confidential-computing work describes TEEs as protecting secrets from other software on the host, including privileged software such as the operating system, hypervisor, and firmware. [3]
The size of that boundary varies. Some technologies protect a small application component, often called an enclave. Others protect an entire confidential virtual machine. A smaller boundary can reduce the amount of code that needs special treatment, while a larger one can make it easier to move an existing workload. Neither is automatically the better security choice; the decision should follow the data, threat model, and operational constraints.
### Memory protection is part of the mechanism
A confidential-computing platform typically uses hardware-backed memory protection so that protected memory is not simply readable by ordinary host software. For example, Intel describes Trust Domain Extensions (TDX) as a hardware-based TEE for hardware-isolated virtual machines and says that its design uses hardware extensions for memory encryption and protects the confidentiality and integrity of trust-domain CPU state. AMD describes Secure Encrypted Virtualization (SEV) as a confidential-VM approach that uses a per-VM key and isolates guests from the hypervisor. [4] [5]
These are examples of architecture-specific implementations, not interchangeable guarantees. A security review should check the chosen processor generation, firmware, host configuration, guest software, and documented threat model rather than treating the label “confidential” as a complete answer.
### Attestation verifies what is about to receive a secret
Remote attestation is the step that makes the boundary useful to a party outside it. A TEE can produce signed evidence, often called measurements or claims, about its origin and current state. A relying party evaluates that evidence and decides whether the environment is the expected hardware and approved workload before releasing a key, credential, or sensitive input. [3]
A simplified sequence looks like this:
A protected workload starts inside a TEE.
The TEE produces attestation evidence tied to its measured configuration.
A verifier checks that evidence against an approved policy.
Only if the check passes does a key-management system or other relying party release the material needed for processing.
This is more than a “secure box” metaphor. The value depends on a real policy: which measurements are approved, who updates them, how evidence freshness is evaluated, which keys may be released, and what happens when verification fails. NIST notes that evidence freshness and replay protections are technology-dependent considerations. [3]
### Keys should follow the trust decision
The practical security benefit is strongest when secret release is bound to attestation. If an encryption key is delivered to an unverified workload before its identity is checked, the system weakens its own boundary. NIST’s prototype work describes a relying party wrapping secrets for a TEE after it evaluates attestation evidence. [3]
That means confidential computing intersects with identity and key management. A team still needs defined key owners, rotation and revocation processes, recovery plans, and audit records. The TEE can help constrain where a secret is used; it does not remove the responsibility to govern the secret’s lifecycle.
What confidential computing can and cannot protect
A clear threat model is more valuable than a broad claim of “complete security.” In many TEE designs, the intended protection is against unauthorised access or modification by other applications, host software, privileged operators, or infrastructure layers outside the TEE. The Consortium distinguishes data confidentiality, data integrity, and code integrity as relevant properties, while also noting that the features available can vary by implementation. [1]
What it can help with:
Reducing exposure of selected data while it is processed in a cloud or shared-compute environment.
Checking that an approved workload configuration is running before a key or secret is released.
Isolating sensitive portions of analytics, key handling, or AI workflows from more of the host software stack.
What it does not solve on its own:
A bug, malicious instruction, or over-broad permission inside the approved application.
A user or service that is legitimately authorised to export data but should not be.
Data sent out by the workload after it has been processed.
Availability attacks. The Consortium states that denial-of-service and distributed-denial-of-service attacks are outside the threat model of current hardware-based TEEs. [1]
Security operations such as vulnerability management, identity governance, network segmentation, backup recovery, and incident response.
The last point is easy to miss. A protected enclave can be the right place to process a secret, but the surrounding application still has interfaces, logs, dependencies, administrators, and failure modes. Treating a confidential-computing boundary as permission to neglect them creates a false sense of safety.
Confidential computing in cloud, analytics, and AI workloads
Confidential computing is a design option when the sensitivity of active data is the central problem. It may be considered for analytics across organisational boundaries, handling cryptographic keys, or processing selected inputs in an AI pipeline. NIST’s initial public draft IR 8320E, published on 29 May 2026, describes an example approach for protecting datasets acted on by AI workloads in cloud infrastructure. That draft is informative context, not final NIST guidance. [7]
For confidential AI, the question is not simply whether a model runs in a TEE. A useful design review follows the sensitive material through the whole path: training or retrieval data, prompts, model weights where relevant, inference inputs, outputs, keys, logs, and connections to accelerators or external tools. A TEE may improve one part of that path while another component remains the dominant exposure.
Illustrative scenario, not a claim about a deployed service: two organisations want to compute a joint fraud signal without giving routine infrastructure administrators access to the raw input records. They could design a workflow in which a verifier approves a measured workload and releases decryption material only to that workload. The outcome still depends on the rules governing data sharing, the input quality, the application’s output controls, and every participant’s legal and security obligations. Confidential computing changes the technical trust boundary; it does not make the partnership automatically permissible or safe.
India context: a technical control, not a legal conclusion
Date-sensitive regulatory context — checked 13 October 2026: India’s Digital Personal Data Protection Act, 2023 applies to specified processing of digital personal data within India and, in certain circumstances, to processing outside India connected with offering goods or services to Data Principals in India. Section 8 requires a Data Fiduciary to implement appropriate technical and organisational measures and to take reasonable security safeguards to prevent a personal data breach. It also places responsibility on the Data Fiduciary for processing undertaken by it or on its behalf. [8]
Observed fact: the Act does not name confidential computing as a required technology in the cited provisions. [8]
Editorial interpretation: confidential computing may be one technical control worth assessing when a system needs to limit infrastructure-level exposure during processing. It cannot by itself establish lawful processing, valid consent, purpose limitation, retention compliance, contractual responsibilities, or breach handling. Organisations should obtain advice appropriate to their facts rather than treating a hardware feature as a legal conclusion.
There is also an operational dimension. Date-sensitive regulatory context — checked 13 October 2026: CERT-In’s 28 April 2022 Directions state that specified entities must report listed cyber incidents within six hours of noticing them or being informed of them, and require secure retention of ICT system logs for a rolling 180 days within Indian jurisdiction. [9] A confidential-workload design therefore needs observability and incident procedures that remain effective without carelessly copying sensitive payloads into logs. Whether and how a specific organisation is covered requires its own current legal and compliance assessment.
Observed fact: Gartner lists confidential computing among its 2026 strategic technology trends and characterises it as protecting sensitive data while in use for AI and analytics across untrusted infrastructure. [10]
Editorial interpretation: that is a useful signal that the topic is receiving strategic attention, not evidence that every Indian organisation should deploy it or a forecast of adoption, availability, cost, or regulatory outcome.
Trade-offs and limitations to plan for
Confidential computing changes engineering constraints as well as security properties. A production design needs to make those constraints visible before a sensitive workload depends on them.
### The trusted computing base still matters
A TEE reduces the set of components that must be trusted for a particular task; it does not reduce it to zero. Hardware roots of trust, firmware, microcode, the TEE implementation, the approved workload, attestation verification, and key-release policy all matter. The protected code itself may be small or large, and a larger protected software base can be harder to inspect and update safely.
### Attestation policy becomes an operational dependency
A team must manage approved measurements and planned changes. A security patch, new library, rebuilt container, or changed kernel may alter the evidence that attestation produces. If policy is too loose, the check becomes less meaningful. If it is too rigid, valid updates can interrupt service. Plan for policy ownership, testing, key recovery, revocation, and change approvals.
### Isolation can reduce convenience
Highly isolated environments may intentionally limit storage, networking, debugging, and interactive administration. AWS’s Nitro Enclaves documentation, for example, describes enclaves as constrained virtual machines with no persistent storage, interactive access, or external networking; they communicate with the parent instance through secure local sockets. It also supports attestation. [6] That is a useful illustration of an engineering trade-off, not a recommendation of a particular service.
### Performance and compatibility are workload-specific
The cost of a confidential-computing design cannot be inferred from the term alone. It depends on the platform, workload, memory pattern, I/O path, virtualisation layer, accelerator use, programming model, and operational design. Measure representative workloads and failure behavior in a controlled evaluation. Do not assume a claimed performance result from another processor, cloud configuration, or application will apply to yours.
How to evaluate a confidential-computing use case
Start with a decision, not a product catalogue. These questions help determine whether confidential computing addresses a material risk:
Which data is sensitive while it is being processed? Map inputs, intermediate values, keys, outputs, and diagnostic data.
Which actor or layer is outside the intended trust boundary? Be specific: another tenant, host administrator, cloud control plane, a compromised operating system, or something else.
What must the TEE protect: a small component or an entire VM? Choose the boundary that fits the workload and the review capacity.
How will attestation be verified? Define the expected measurements, freshness checks, verifier, approval process, and failure response.
When are keys released, rotated, and revoked? Bind key release to a successful trust decision where appropriate, and test recovery paths.
What remains outside the TEE? Review interfaces, logs, storage, network endpoints, identities, administrator actions, and output controls.
How will the system be operated during an incident? Confirm that logging, monitoring, patching, and response procedures preserve useful evidence without unnecessarily exposing sensitive data.
A pilot should test the security claim and the operational claim together. For example, it should demonstrate that an unapproved measurement cannot obtain a protected key, while also showing how legitimate updates, monitoring, and recovery actually work.
Frequently asked questions
### Is confidential computing the same as encryption?
No. Encryption is a core mechanism, but confidential computing is a broader hardware-enabled design for protecting code and data while they are in use. It commonly combines isolated execution, memory protection, attestation, and a policy for handling secrets. [1] [3]
### What is a trusted execution environment?
A TEE is an isolated execution area designed to protect selected code and data from other software on the host. Its exact boundary and guarantees vary by implementation, so the specific platform documentation and threat model matter. [1] [3]
### What is the difference between a secure enclave and a confidential VM?
An enclave usually refers to a smaller protected application area, while a confidential VM protects a virtual-machine-sized workload boundary. Both can be TEE-based approaches, but their programming model, trusted code size, integration work, and security properties differ. [1] [4] [5]
### How does remote attestation work?
A TEE produces signed evidence about its identity and state. A verifier checks that evidence against policy and can decide whether to trust the environment, such as by releasing a key to it. Details such as evidence freshness and replay protection are technology-dependent. [3]
### Can confidential computing stop a cloud provider from seeing data?
It can be designed to reduce the ability of host-side software and infrastructure operators to inspect selected data in the protected workload. It does not eliminate all trust, and it does not protect data that authorised application code intentionally sends outside the boundary. The actual answer depends on the selected implementation and configuration. [1] [4] [5]
### Does confidential computing replace zero trust?
No. Zero trust covers decisions about identity, device posture, access, segmentation, verification, and monitoring. Confidential computing can strengthen one execution boundary, but it does not replace identity or authorization controls. See the related TechDuoPulse zero-trust explainer for the wider control model.
### Does confidential computing make an AI system private or compliant?
Not automatically. It may help protect selected inputs, models, or processing steps, but privacy and compliance also involve lawful purpose, access policy, retention, output handling, contracts, governance, and incident response. India’s DPDP Act provisions cited here do not prescribe confidential computing. [7] [8]
### What kinds of workloads are good candidates?
A candidate workload has a clearly identified data-in-use risk and a feasible way to define, attest, and operate a protected boundary. Sensitive analytics, key-related operations, and selected AI processing paths can be candidates, but suitability depends on the threat model and operational constraints rather than on a general industry label. [1] [7]
Internal-link recommendations — private editorial guidance
Use only where the surrounding copy makes the relationship useful. These are recommendations for the eventual published article, not assertions that links are already live.
Link “zero-trust controls” in the limits section to /article/zero-trust-five-controls to clarify that TEEs complement identity and access verification.
Link “cloud identity and active sessions” in the key-release discussion to /article/cloud-identity-attacks-token-theft-session-security for the identity/token dimension of confidential workloads.
Link “AI agents and permission boundaries” in the confidential-AI section to /article/ai-agents-permission-boundaries-audit-logs when discussing tool access outside a TEE.
Link “RAG production failure modes” in the AI path review to /article/retrieval-augmented-generation-production-failure-modes for retrieval permissions, provenance, and evaluation.
Link “software supply-chain provenance” in the attestation-policy section to /article/software-supply-chain-sbom-build-provenance because trusted measurements depend on knowing what was built and deployed.
Link “multi-region failure domains and data consistency” in the recovery discussion to /article/multi-region-architecture-failure-domains-data-consistency where the final content expands on availability and recovery limits.
Frequently asked questions about Confidential Computing Explained: Protecting Data While It Is Being Used
These answers summarise the scope of this explainer. Availability, standards and implementation details can change, so check current official guidance before acting.
What is Confidential Computing Explained: Protecting Data While It Is Being Used?
Confidential Computing Explained: Protecting Data While It Is Being Used explains the main ideas, practical uses and limitations in plain English.
Why does this technology matter?
Its value depends on the problem, implementation, evidence, cost, security and the people responsible for using it.
What should readers verify?
Verify current availability, compatibility, security, privacy and regulatory details with the relevant official source.
Is this article professional or legal advice?
No. It is general technology information and does not replace professional, legal, regulatory or security advice.
Source notes
Reporting record
techduopulse stores source destinations privately. Public notes remain non-clickable so every visitor journey stays on this website.
Gartner Top 10 Strategic Technology Trends for 2026
Primary source · Research source 10Confidential Computing Consortium: Confidential Computing — Hardware-Based Trusted Execution for Applications and Data
Primary source · Research source 1NIST IR 8320: Hardware-Enabled Security — Enabling a Layered Approach to Platform Security for Cloud and Edge Computing Use Cases
Primary source · Research source 2NIST IR 8320D Initial Public Draft: Hardware-Enabled Security — Hardware-Based Confidential Computing
Primary source · Research source 3Intel Trust Domain Extensions Overview
Primary source · Research source 4AMD Secure Encrypted Virtualization Overview
Primary source · Research source 5AWS Nitro Enclaves User Guide: What Is Nitro Enclaves?
Primary source · Research source 6NIST IR 8320E Initial Public Draft: Hardware-Enabled Security — Confidential Computing of Data in Cloud Workloads
Primary source · Research source 7The Digital Personal Data Protection Act, 2023
Primary source · Research source 8CERT-In Directions Under Section 70B of the Information Technology Act, 2000
Primary source · Research source 9New India-focused explainer covering Confidential Computing Explained: Protecting Data While It Is Being Used, practical context, limitations and verified sources.